SBA Research is a research center for Information Security funded partly by the national initiative for COMET Competence Centers for Excellent Technologies.
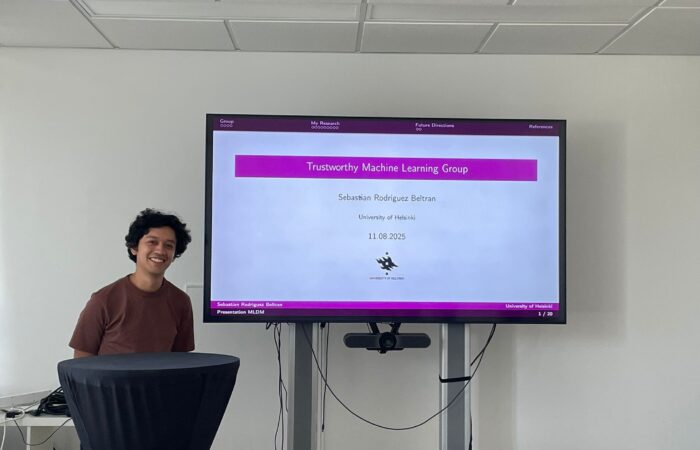
The MLDM team hosted Sebastian Rodriguez Beltran as visiting researcher.
Sebastian is a PhD student under the supervision of Antti Honkela, a professor at the Department of Computer Science, University of Helsinki, and a leading figure in Privacy-Preserving Machine Learning. ... Read More
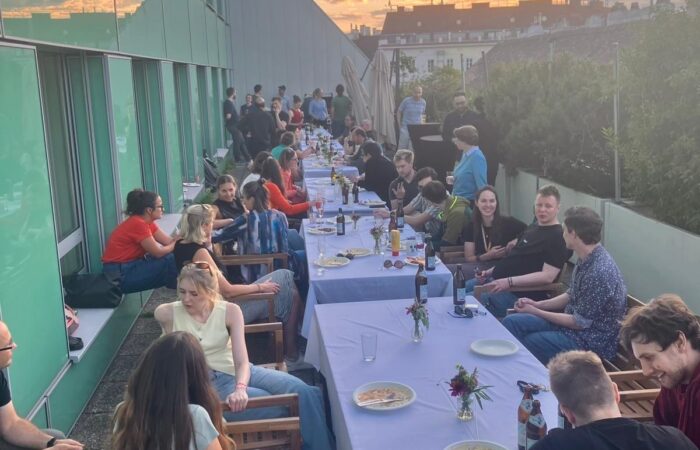
On a warm summer evening end of July, the SBA Research employees and alumni came together for our annual SBA BBQ – a tradition that brings colleagues, friends, and former team members together in a relaxed and welcoming atmosphere. The event offered the perfect opportunity to reconnect with alumni, share… Read More
In June, our colleague Bernhard Garn, senior researcher at SBA Research, participated in the 2nd IRDR Young Scientists Lumos, a global pre-event to the 2025 Global Platform for Disaster Risk Reduction (GPDRR). Co-hosted by the Integrated Research on Disaster Risk (IRDR) and the… Read More
We are proud to announce that this year, three members of SBA Research have been recognized for their outstanding contributions! Each year, the University of Vienna honors exceptional accomplishments by affiliated researchers through its “Best of the Best” awards. The recognition focuses on two main categories:… Read More
Vulnerability Overview All user accounts authenticate towards a Filebrowser instance with a password. A missing password policy and brute-force protection makes it impossible for administrators to properly secure the authentication process. Recommended Countermeasure We recommend to update to Filebrowser version 2.34.1 or later and configure… Read More
Vulnerability Overview Files managed by Filebrowser can be shared with a link to external persons. While the application allows protecting those links with a password, the implementation is error-prone, making an incidental unprotected sharing of a file possible. Recommended Countermeasure We recommend to update to… Read More
Vulnerability Overview The Command Execution feature of Filebrowser only allows the execution of shell commands which have been predefined on a user-specific allowlist. The implementation of this allowlist is erroneous, allowing a user to execute additional commands not permitted. Recommended Countermeasure We recommend to update… Read More
Vulnerability Overview In the web application, all users have a scope assigned, and they only have access to the files within that scope. The Command Execution feature of Filebrowser allows the execution of shell commands which are not restricted to the scope, potentially giving an attacker read and write access… Read More
Vulnerability Overview The Command Execution feature of Filebrowser only allows the execution of shell command which have been predefined on a user-specific allowlist. Many tools allow the execution of arbitrary different commands, rendering this limitation void. Recommended Countermeasure We recommend to disable the… Read More
Vulnerability Overview The Markdown preview function of Filebrowser v2.32.0 is vulnerable to Stored Cross-Site-Scripting (XSS). Any JavaScript code that is part of a Markdown file uploaded by a user will be executed by the browser. Recommended Countermeasure We recommend to update to Filebrowser version 2.33.7… Read More
A new paper, “Systematization of Knowledge: The Design Space of Digital Payment Systems with Potential for CBD,” led by first author Judith Senn, research assistant at the University of Innsbruck, and co-authored by Aljosha Judmayer, researcher at the University of Vienna, Nicholas Stifter, researcher at SBA Research, ... ∞
Last week, our annual event for partners and friends of SBA Research, IMPACT, brought together experts, practitioners, and decision-makers from research, industry, and the open-source community. The afternoon provided an opportunity to discuss the latest developments in security, AI, and innovation, celebrate our long-standing relationships, and mark 20 years of SBA Research’s contributions to cutting-edge cybersecurity and trustworthy digital innovation. ∞
A group of dedicated young researchers presented their work at the 22st ICT Security Conference on 16 and 17 September 2026, which was organized by the Austrian Armed Forces. ∞