SBA Research is a research center for Information Security funded partly by the national initiative for COMET Competence Centers for Excellent Technologies.
The 20th International Conference on Availability, Reliability, and Security (ARES 2025) took center stage in Ghent, Belgium, from August 11-14, 2025, offering a platform for experts and enthusiasts to explore the latest developments in the field. Co-located with ARES 2025 was the 8th International Symposium for Industrial Control System & SCADA Cyber Security Research.... Read More
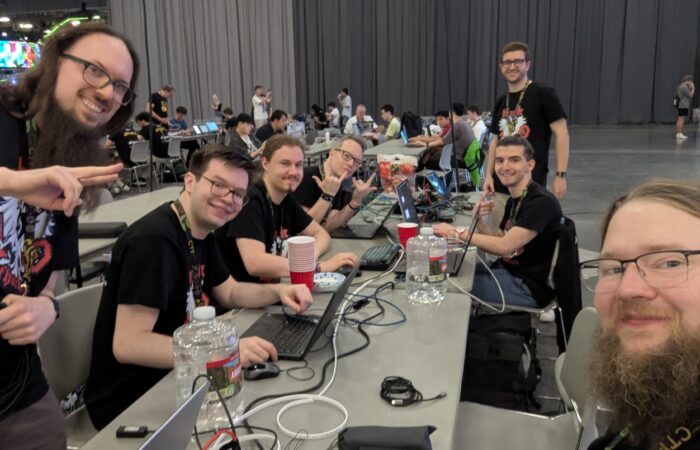
We are incredibly proud of the Austrian hacking team KuK Hofhackerei, which secured 9th place at DEF CON CTF 33, one of the toughest and most renowned Capture the Flag competitions in the world. The DEF CON Capture the Flag competition is… Read More
Vulnerability Overview All user accounts authenticate towards a Filebrowser instance with a password. A missing password policy and brute-force protection makes it impossible for administrators to properly secure the authentication process. Recommended Countermeasure We recommend to update to Filebrowser version 2.34.1 or later and configure… Read More
Vulnerability Overview Files managed by Filebrowser can be shared with a link to external persons. While the application allows protecting those links with a password, the implementation is error-prone, making an incidental unprotected sharing of a file possible. Recommended Countermeasure We recommend to update to… Read More
Vulnerability Overview The Command Execution feature of Filebrowser only allows the execution of shell commands which have been predefined on a user-specific allowlist. The implementation of this allowlist is erroneous, allowing a user to execute additional commands not permitted. Recommended Countermeasure We recommend to update… Read More
Vulnerability Overview In the web application, all users have a scope assigned, and they only have access to the files within that scope. The Command Execution feature of Filebrowser allows the execution of shell commands which are not restricted to the scope, potentially giving an attacker read and write access… Read More
Vulnerability Overview The Command Execution feature of Filebrowser only allows the execution of shell command which have been predefined on a user-specific allowlist. Many tools allow the execution of arbitrary different commands, rendering this limitation void. Recommended Countermeasure We recommend to disable the… Read More
Vulnerability Overview URLs that are accessed by a user are commonly logged in many locations, both server- and client-side. It is thus good practice to never transmit any secret information as part of a URL. Filebrowser violates this practice, since access tokens are used as GET parameters. Read More
Our colleague Sebastian Raubitzek, researcher at SBA Research and a member of the Security and Privacy Research Group at the University of Vienna, has published a journal article titled “Multi-Class Machine Learning to Quantify the Impact of Nitrogen Management Practices on Grassland Biomass” in MDPI’s Journal Nitrogen ... Read More
A group of dedicated young researchers presented their work at the 21st ICT Security Conference on 25 and 26 June 2025, which was organized by the Austrian Armed Forces. They impressed the audience with their… Read More
A new paper, “Automated Reasoning for Indistinguishability in the CCSA,” co-authored by Laura Kovács, key researcher at SBA Research and full professor at the Faculty of Informatics of the Vienna University of Technology (TU Wien), and Matteo Maffei, key researcher at SBA Research and Professor at TU Wien, has been accepted for presentation at the 33rd ACM Conference on Computer and Communications Security (CCS). ∞
The 21th International Conference on Availability, Reliability, and Security (ARES 2026) took center stage in Linköping, Sweden, from August 24 - 27, 2026, offering a platform for experts and enthusiasts to explore the latest developments in the field. The conference was jointly organised by Linköpings universitet (LiU) and SBA Research. ∞
New paper “Send and Pretend: Exploiting Transcript Consistency Issues in End-to-End Encrypted Group Chats”, was recently accepted for the 35th USENIX Security Symposium. The paper is a collaboration between SBA, the University of Vienna, and the Interdisciplinary Transformation University Austria (IT:U). It was authored by Gabriel K. Gegenhuber, Moritz Grefner, Maximilian Günther, Matthäus Wininger, David Schmidt, and Aljosha Judmayer. ∞