SBA Research is a research center for Information Security funded partly by the national initiative for COMET Competence Centers for Excellent Technologies.
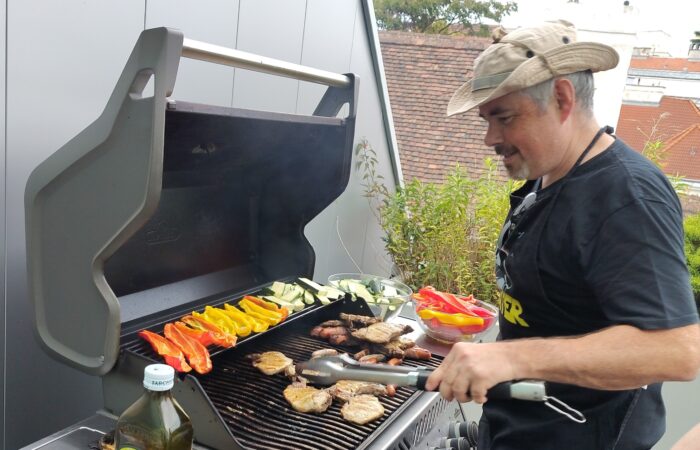
On a warm summer evening in August, we came together for our annual SBA BBQ. A tradition that brings colleagues, friends, and former team members together in a relaxed and welcoming atmosphere. Read More
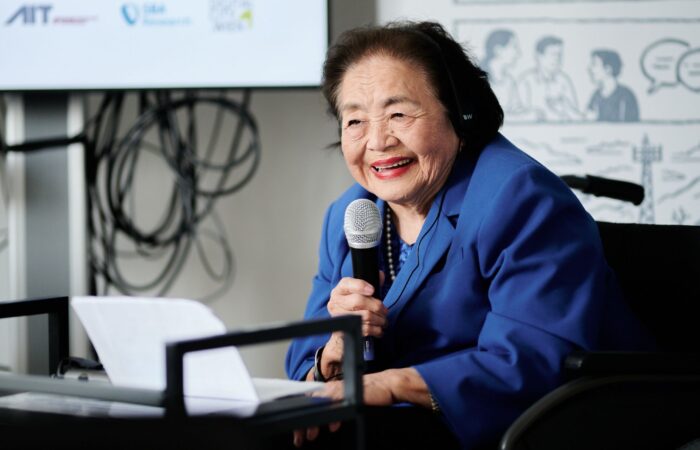
How can technology contribute to peace? And what responsibility do today's innovators carry?
Together with the PeaceTech Alliance and AIT Austrian Institute of Technology, SBA Research had the privilege of welcoming Hiroshima survivor and Nobel Peace Prize laureate Setsuko Thurlow to Vienna for the event "Hiroshima's Message for Tech Students and Innovators Today." Read More
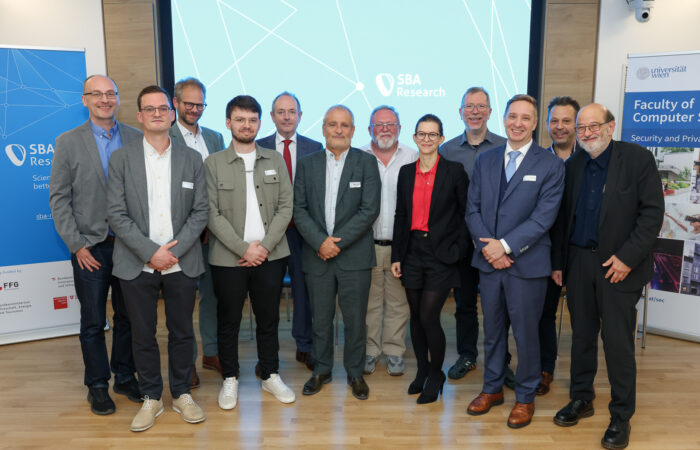
In mid-October, our yearly partner and friends of SBA Research event IMPACT brought together experts, practitioners, and decision-makers from research, industry, and the open-source community. One afternoon with discussion about the latest developments in security, open source, and research and to celebrate our long-standing relationships. This year’s program… Read More
On a warm summer evening end of July, the SBA Research employees and alumni came together for our annual SBA BBQ – a tradition that brings colleagues, friends, and former team members together in a relaxed and welcoming atmosphere. The event offered the perfect opportunity to reconnect with alumni, share… Read More
The 21th International Conference on Availability, Reliability, and Security (ARES 2026) took center stage in Linköping, Sweden, from August 24 - 27, 2026, offering a platform for experts and enthusiasts to explore the latest developments in the field. The conference was jointly organised by Linköpings universitet (LiU) and SBA Research. ∞
New paper “Send and Pretend: Exploiting Transcript Consistency Issues in End-to-End Encrypted Group Chats”, was recently accepted for the 35th USENIX Security Symposium. The paper is a collaboration between SBA, the University of Vienna, and the Interdisciplinary Transformation University Austria (IT:U). It was authored by Gabriel K. Gegenhuber, Moritz Grefner, Maximilian Günther, Matthäus Wininger, David Schmidt, and Aljosha Judmayer. ∞
The IRIS web application in version 2.4.26 and possibly others is vulnerable to stored cross-site scripting (XSS) in the assets (CVE-2026-16969), custom attributes (CVE-2026-18360) and datastore upload (CVE-2026-18361) functions. ∞