SBA Research is a research center for Information Security funded partly by the national initiative for COMET Competence Centers for Excellent Technologies.
Sebastian Schrittwieser, key researcher at SBA Research and head of the CD-Lab AsTra and Johanna Ullrich, key researcher at SBA Research and Professor of Security at IT:U, received the Best Paper Award at the AgentSkills Workshop at the ACM Conference on AI and Agentic Systems (CAIS 2026) in San José for their work Context Matters: Repository-Aware Security Analysis of the Agent Skill Ecosystem. Read More
On 20–21 May 2026, SBA Research had the pleasure of hosting the ERCIM Spring Meeting at our offices in Vienna. Representatives from ERCIM member institutions across Europe came together for two days of exchange, strategic discussions, and collaborative planning focused on the future of European research in informatics and mathematics. Read More
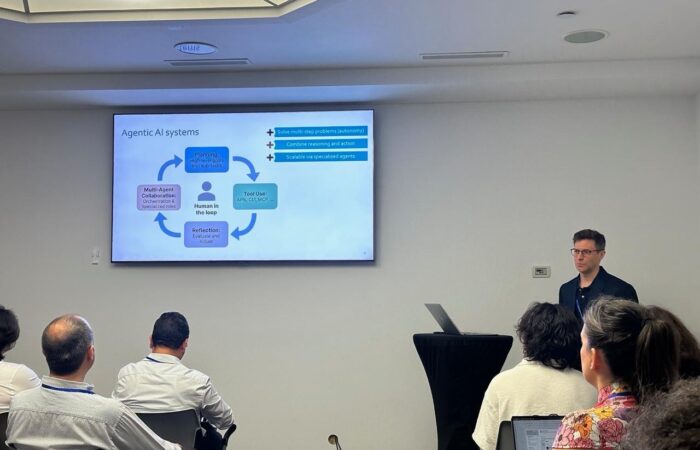
Our colleague Andreas Ekelhart, key researcher and Applied Research Lead at SBA Research and researcher at the Research Group Security & Privacy at University of Vienna,, presented his conference paper titled AgentO: An Ontology for Modeling Agentic AI Systems at the 23rd European Semantic Web Conference (ESWC 2026) in Dubrovnik, Croatia. Read More
Our colleague Sebastian Raubitzek, researcher at SBA Research and a member of the Security and Privacy Research Group at the University of Vienna, has published a journal article titled “Fractals in Neural Networks: Introducing a New Class of Activation Functions” in Communications in Nonlinear Science and Numerical Simulations in collaboration with the CD lab AsTra. Read More
Users can create alerts for customers that are not assigned to them. This can be abused to falsely attribute fake alerts to customers. In combination with Cross-Site Scripting, this can also be used to exfiltrate alerts from other customers. Read More
The IRIS web application is vulnerable to a Cross-site request forgery attack, because it uses the HTTP method GET to change state on the server. Read More
The IRIS web application does not properly validate uploaded files. It can therefore be misused to host phishing pages, amongst other things. This also creates an instance of a Cross-Site Scripting (XSS) vulnerability. Read More
The IRIS web application contains a weakness where an attacker can misuse it to redirect the user to a malicious website controlled by an attacker. Read More
A new paper, “Automated Reasoning for Indistinguishability in the CCSA,” co-authored by Laura Kovács, key researcher at SBA Research and full professor at the Faculty of Informatics of the Vienna University of Technology (TU Wien), and Matteo Maffei, key researcher at SBA Research and Professor at TU Wien, has been accepted for presentation at the 33rd ACM Conference on Computer and Communications Security (CCS). ∞
The 21th International Conference on Availability, Reliability, and Security (ARES 2026) took center stage in Linköping, Sweden, from August 24 - 27, 2026, offering a platform for experts and enthusiasts to explore the latest developments in the field. The conference was jointly organised by Linköpings universitet (LiU) and SBA Research. ∞
New paper “Send and Pretend: Exploiting Transcript Consistency Issues in End-to-End Encrypted Group Chats”, was recently accepted for the 35th USENIX Security Symposium. The paper is a collaboration between SBA, the University of Vienna, and the Interdisciplinary Transformation University Austria (IT:U). It was authored by Gabriel K. Gegenhuber, Moritz Grefner, Maximilian Günther, Matthäus Wininger, David Schmidt, and Aljosha Judmayer. ∞