SBA Research is a research center for Information Security funded partly by the national initiative for COMET Competence Centers for Excellent Technologies.
The IRIS web application is vulnerable to a Cross-site request forgery attack, because it uses the HTTP method GET to change state on the server. Read More
The IRIS web application does not properly validate uploaded files. It can therefore be misused to host phishing pages, amongst other things. This also creates an instance of a Cross-Site Scripting (XSS) vulnerability. Read More
The IRIS web application contains a weakness where an attacker can misuse it to redirect the user to a malicious website controlled by an attacker. Read More
This May, SBA Research opens its doors to the European research community. From 20–21 May 2026, we are hosting the ERCIM Spring Meetings at our Vienna offices, welcoming representatives from member institutions across Europe for two days of strategic discussions, board deliberations, and collaborative exchange. It is a moment we have been looking forward to, and one that reflects the strength of the partnerships we have built over the years within ERCIM. Read More
In April, our colleague Anastasia Pustozerova is researcher at SBA Research and has published a journal article titled “Lightweight Techniques for Federated Anomaly Detection in Log Data” in IEEE Transactions on Reliability. Read More
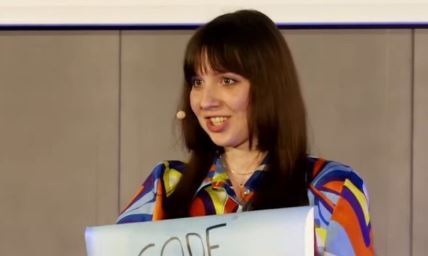
Our colleague Caroline König, researcher at SBA Research and research assistant at the CD-Lab AsTra took part in the CDG-Science-Slam and presented her research on software protection. Within just a few minutes, she gave attendees an entertaining and accessible look at the challenges of shielding software from analysis and tampering, a topic that has become increasingly critical in today's security landscape. Read More
GoAnywhere MFT before 7.10.0 is affected by an HTML injection vulnerability in its email templating functionality. If an attacker is able to influence the content of a template variable, malicious HTML can be embedded into outgoing emails generated by the application. As these messages originate from a trusted system, the vulnerability may facilitate phishing and other social-engineering attacks. The issue arises from insufficient HTML encoding of untrusted input before inclusion in HTML email content. Read More
Last week, our annual event for partners and friends of SBA Research, IMPACT, brought together experts, practitioners, and decision-makers from research, industry, and the open-source community. The afternoon provided an opportunity to discuss the latest developments in security, AI, and innovation, celebrate our long-standing relationships, and mark 20 years of SBA Research’s contributions to cutting-edge cybersecurity and trustworthy digital innovation. ∞
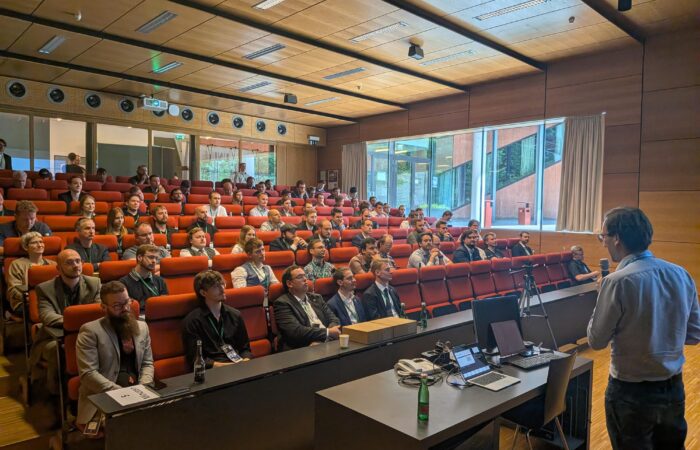
A group of dedicated young researchers presented their work at the 22st ICT Security Conference on 16 and 17 September 2026, which was organized by the Austrian Armed Forces. ∞
A new paper, “Automated Reasoning for Indistinguishability in the CCSA,” co-authored by Laura Kovács, key researcher at SBA Research and full professor at the Faculty of Informatics of the Vienna University of Technology (TU Wien), and Matteo Maffei, key researcher at SBA Research and Professor at TU Wien, has been accepted for presentation at the 33rd ACM Conference on Computer and Communications Security (CCS). ∞